Aether server
This page sets up a server for Aether's Private mode on Ubuntu 24.04. The server runs our Aether engine in a Docker container, which carries the phones' traffic on to Cloudflare WARP, and WireGuard, which the phones use to reach it. A phone reaches only the engine's SOCKS5 port on the server's tunnel address, so the server needs no forwarding and no NAT. Public mode needs none of this. Its last part sets up the profile in the app, on iPhone and on Android.
We ran these steps on our test server, Ubuntu 24.04.5 with Linux 6.8, Docker 29.1.3 and wireguard-tools 1.0.20210914 from Ubuntu's packages, 12 vCPUs and 32 GB of memory, on 9 November 2026, as the page shows them, with our server's name in place of vpn.example.com; part 6 made iphone1, android1 and phone2, and part 7 removed phone2. The round's test setup had been moved aside first. Part 1's packages were already there, and part 2 took the image from Docker's cache: it had been built with the same command that day, in about 20 minutes. The volume aether-data already held a WARP identity, which the engine kept. After a restart of wg-quick@wg0 the server still had iphone1 and android1 (SaveConfig). With Docker and wg0 both stopped, starting Docker started wg0 first, and the container listened on 10.66.66.1 again. Then both phones connected with the page's own files, and phone2's file was refused (cases ae-guide-… of Test results).
What you need
- An Ubuntu 24.04 server with a public IPv4 address, and root access to it. Its kernel has WireGuard built in.
- UDP port 51820 open to the phones. A DNS name for the server is optional: the phones' files can name the server or its address.
- The server must reach Cloudflare WARP over UDP port 443, which MASQUE on HTTP/3 uses.
1. Install
apt update
apt install -y wireguard docker.io git
This installs WireGuard's tools wg and wg-quick, Docker from Ubuntu's packages, and git, which Docker uses to fetch the engine's source in the next step.
2. The Aether engine
docker build -t srp-aether:v2.4.0-srp.2 "https://github.com/bigmoveus/Aether.git#v2.4.0-srp.2"Docker fetches the tag v2.4.0-srp.2 of our fork and builds the engine, with Tor and its helpers, into the image srp-aether:v2.4.0-srp.2. On our server, with 12 vCPUs, the build took about 20 minutes, and the image is 34 MB.
3. The server's keys and wg0
cd /etc/wireguard
umask 077
wg genkey | tee server.key | wg pubkey > server.pub
cat > /etc/wireguard/wg0.conf <<EOF
[Interface]
Address = 10.66.66.1/24
ListenPort = 51820
PrivateKey = $(cat /etc/wireguard/server.key)
SaveConfig = true
EOF
systemctl enable --now wg-quick@wg0
wg show wg0server.keyis the server's private key andserver.pubits public key, which every phone's file names.umask 077makes the keys readable by root only.Address = 10.66.66.1/24is the server's address inside the tunnel, and the phones get other addresses in 10.66.66.0/24. The server's address must end in.1: the app looks for the engine at the first address of the phone's network, for example 10.66.66.1 for a phone with 10.66.66.2.SaveConfig = trueletswg-quick savewrite the phones that part 6 adds back into this file, so they come back after a restart.- There are no forwarding or NAT rules: the phones' packets do not leave the server. The engine opens its own connections to WARP.
wg show prints the interface with its public key and listening port: 51820.
4. The Aether container
mkdir -p /etc/systemd/system/docker.service.d
cat > /etc/systemd/system/docker.service.d/wg0.conf <<EOF
[Unit]
Wants=wg-quick@wg0.service
After=wg-quick@wg0.service
EOF
systemctl daemon-reload
docker run -d --name aether --restart unless-stopped \
  -e AETHER_PROTOCOL=masque -e AETHER_SCAN=balanced -e AETHER_NOIZE=firewall -e AETHER_QUICK_RECONNECT=1 -e AETHER_TLS_VERIFY=1 \
  -v aether-data:/data -p 10.66.66.1:1819:1819 srp-aether:v2.4.0-srp.2
docker logs aether
-p 10.66.66.1:1819:1819publishes the engine's SOCKS5 port on wg0's address only, so only phones connected over WireGuard reach it. Never publish it on every address: the engine takes every connection without a password, so it would be an open proxy. The engine's log warns that its listener is reachable from outside this machine; here, that means only from wg0.- The file in
docker.service.dstarts Docker after wg0. Otherwise, after a reboot, the container could start before 10.66.66.1 exists and could not listen on it. - The volume
aether-datakeeps the WARP identity the engine registers when it first starts.--restart unless-stoppedstarts the container again after a restart of Docker or of the server. AETHER_PROTOCOL=masquemakes the engine reach WARP over MASQUE, andAETHER_TLS_VERIFY=1makes it check the WARP edge's certificate against the pins it carries, as the apps do. The other three settings make it start without asking questions: Configuration Reference explains them.
Within seconds, the log shows masque tunnel validated (end-to-end data confirmed); exposing socks5 and socks5 server listening on 0.0.0.0:1819. That is the container's own address, which Docker publishes on 10.66.66.1.
5. Firewall
Open UDP port 51820 to the phones. If ufw is active, run ufw allow 51820/udp. The SOCKS5 port needs no rule, because Docker publishes it on 10.66.66.1, an address that only the phones in the tunnel reach.
6. A file for each phone
Each phone gets its own key pair and its own preshared key, which adds a second secret to the handshake. The script below makes them, adds the phone to wg0, and writes the file the app imports. Save it as /etc/wireguard/add-phone.sh, and put your server's name or address in endpoint=:
#!/bin/bash
# add-phone.sh NAME NUMBER: a key pair and a preshared key for the phone NAME, its peer on wg0 with the address
# 10.66.66.NUMBER, and /etc/wireguard/clients/NAME.conf, the file the app imports in Private mode.
set -euo pipefail
name=$1; number=$2; endpoint=vpn.example.com:51820
cd /etc/wireguard
umask 077
mkdir -p clients
private=$(wg genkey); public=$(echo "$private" | wg pubkey); psk=$(wg genpsk)
echo "$public" > "clients/$name.pub"
wg set wg0 peer "$public" preshared-key <(echo "$psk") allowed-ips "10.66.66.$number/32"
wg-quick save wg0
cat > "clients/$name.conf" <<EOF
[Interface]
PrivateKey = $private
Address = 10.66.66.$number/32

[Peer]
PublicKey = $(cat server.pub)
PresharedKey = $psk
Endpoint = $endpoint
AllowedIPs = 10.66.66.1/32
PersistentKeepalive = 25
EOF
echo "/etc/wireguard/clients/$name.conf"
chmod 700 /etc/wireguard/add-phone.sh
/etc/wireguard/add-phone.sh phone1 2- The script prints the file's name, here
/etc/wireguard/clients/phone1.conf. The file holds the phone's private key, so whoever has it can connect as that phone. Copy it to the phone, import it in the app (Import Config), and delete the copies you do not need. AllowedIPs = 10.66.66.1/32is all the phone needs, because it reaches only the engine. There is noDNSline: names are looked up through the engine too. Configuration Reference explains the other lines.PersistentKeepalive = 25makes the phone send a keepalive every 25 seconds when nothing else is sent, so routers between the phone and the server keep its path open.- Give each phone its own number and its own file.
7. Removing a phone
This script takes a phone off wg0 at once and out of the saved configuration. Save it as /etc/wireguard/remove-phone.sh:
#!/bin/bash
# remove-phone.sh NAME: the phone NAME off wg0 and out of wg0.conf, and its files deleted.
set -euo pipefail
name=$1
cd /etc/wireguard
wg set wg0 peer "$(cat "clients/$name.pub")" remove
wg-quick save wg0
rm -f "clients/$name.pub" "clients/$name.conf"
chmod 700 /etc/wireguard/remove-phone.sh
/etc/wireguard/remove-phone.sh phone2The server answers nothing to a key it does not know, so a removed phone cannot connect. The app waits for the handshake, then reports that the server did not answer it.
8. Check
wg show wg0
docker logs --tail 20 aether
curl --socks5-hostname 10.66.66.1:1819 https://www.cloudflare.com/cdn-cgi/trace
Each phone is a peer with its allowed ips. A phone that has connected also has an endpoint, a latest handshake and its transfer. The last command goes through the engine from the server itself: its answer has the line warp=on.
9. Set up the app on the phone
An Aether profile has the same fields on iPhone and Android; where the two phones differ, the steps say so. Install the app first: on iPhone from TestFlight (Installation), on Android by building it from the source (Installation). Where to start says which build to use.
Create the profile
- Copy
/etc/wireguard/clients/phone1.conf, the file part 6 made, to the phone. - On the home screen, tap +.
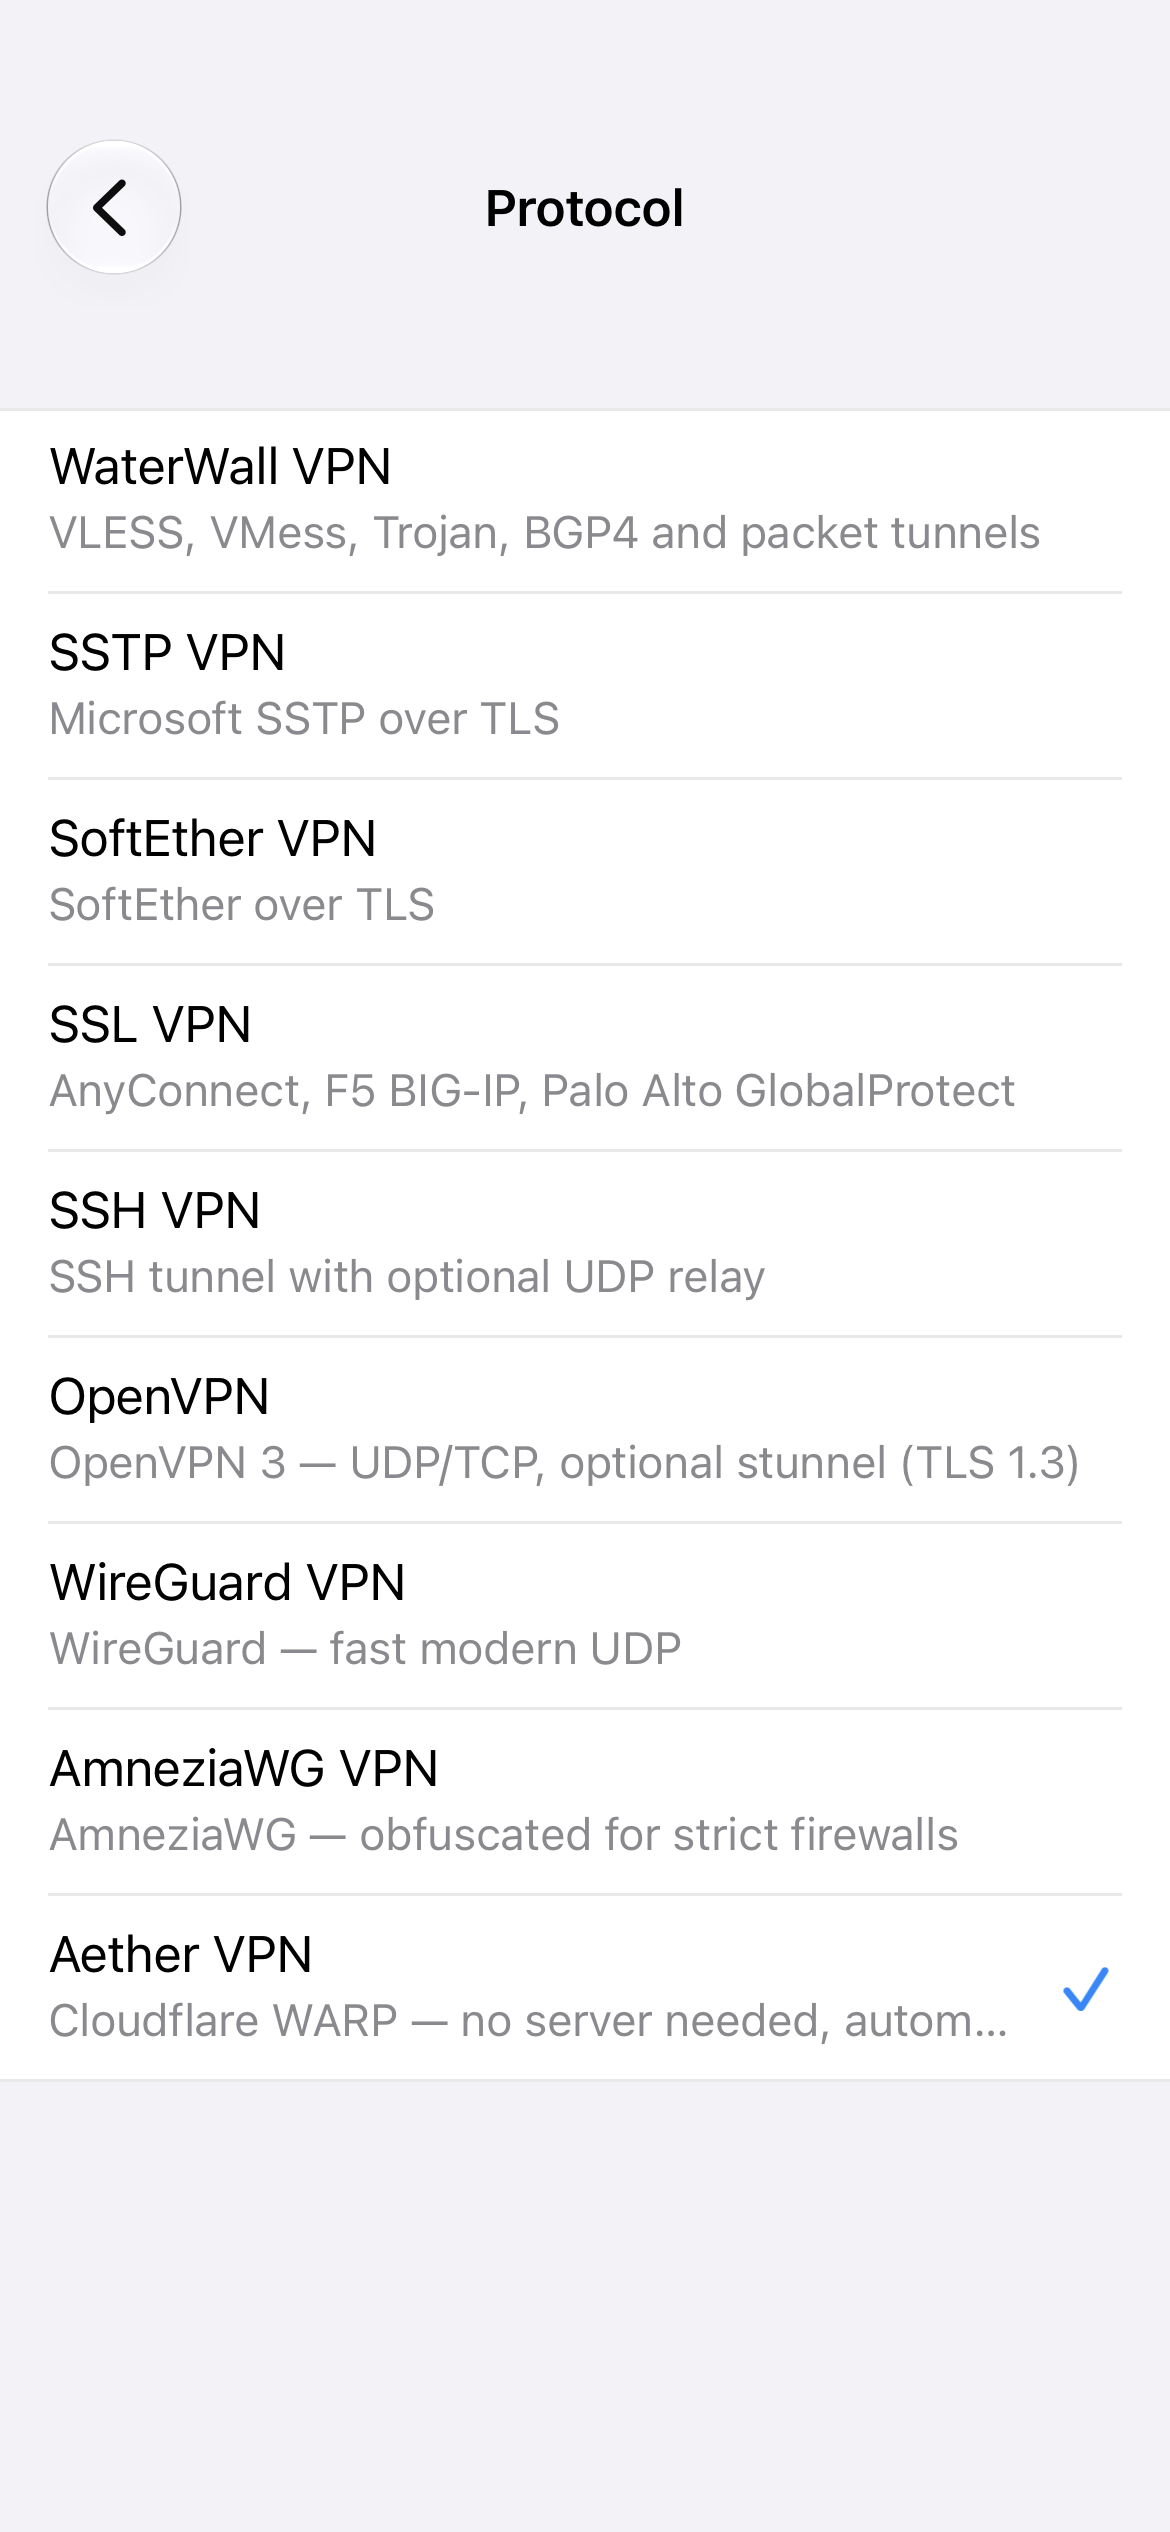
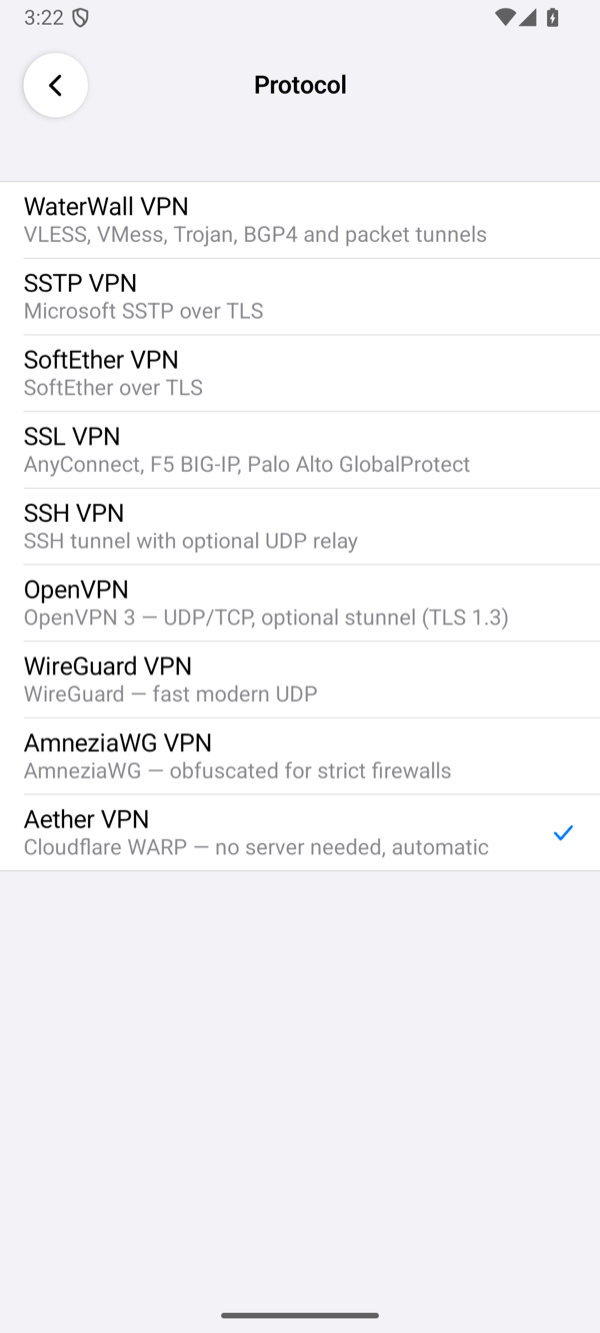
- Tap Protocol and choose Aether VPN. A new Aether profile is in Public mode.
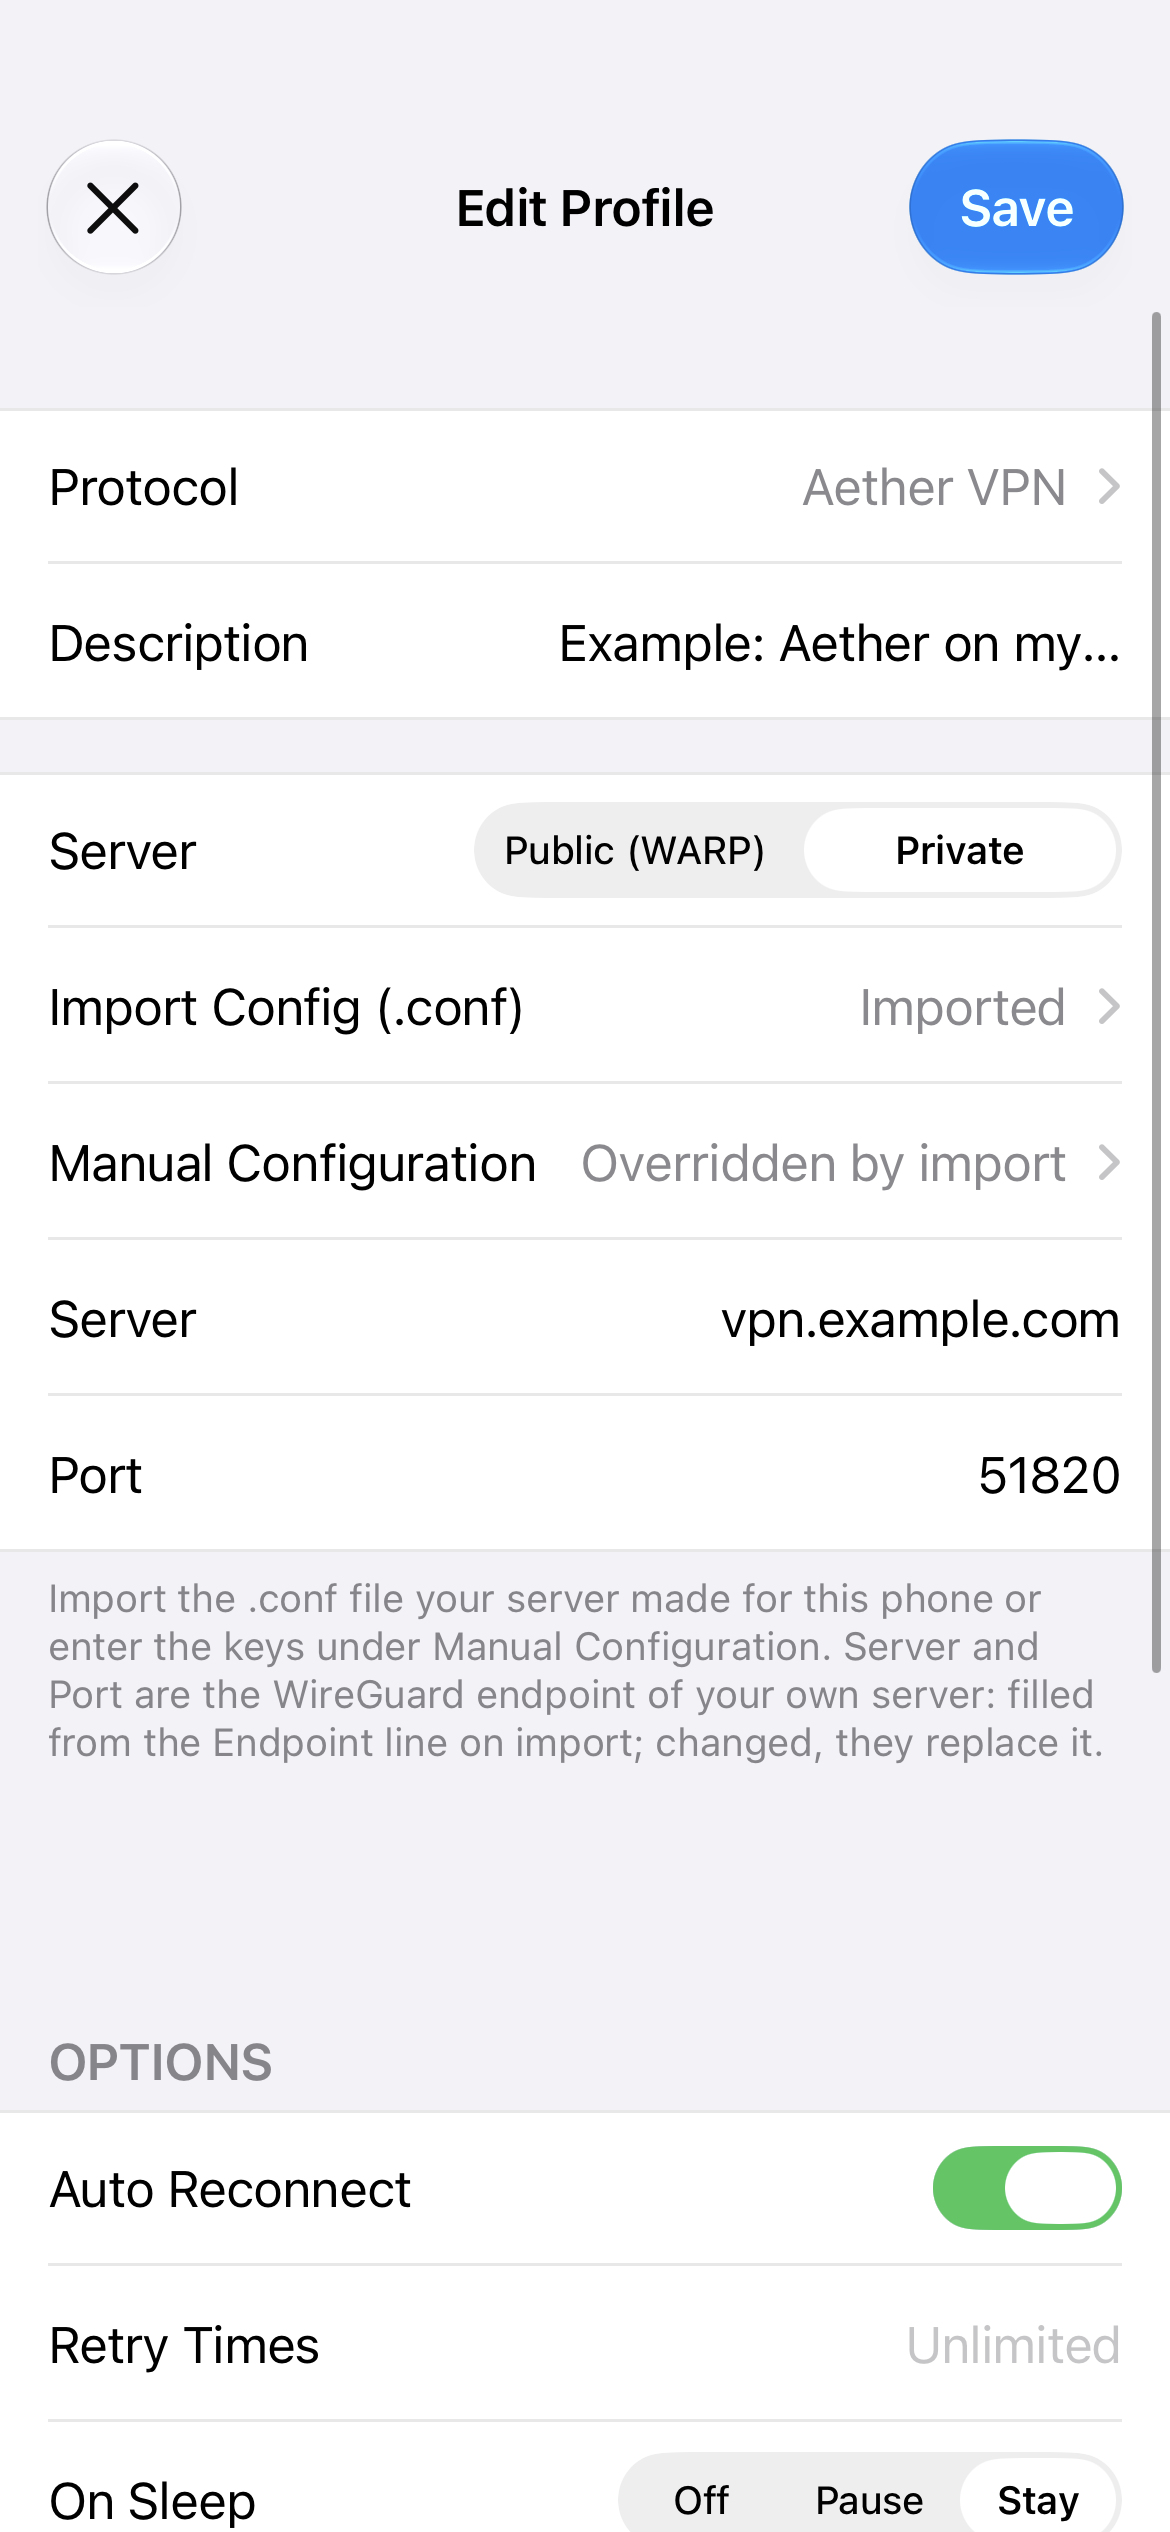
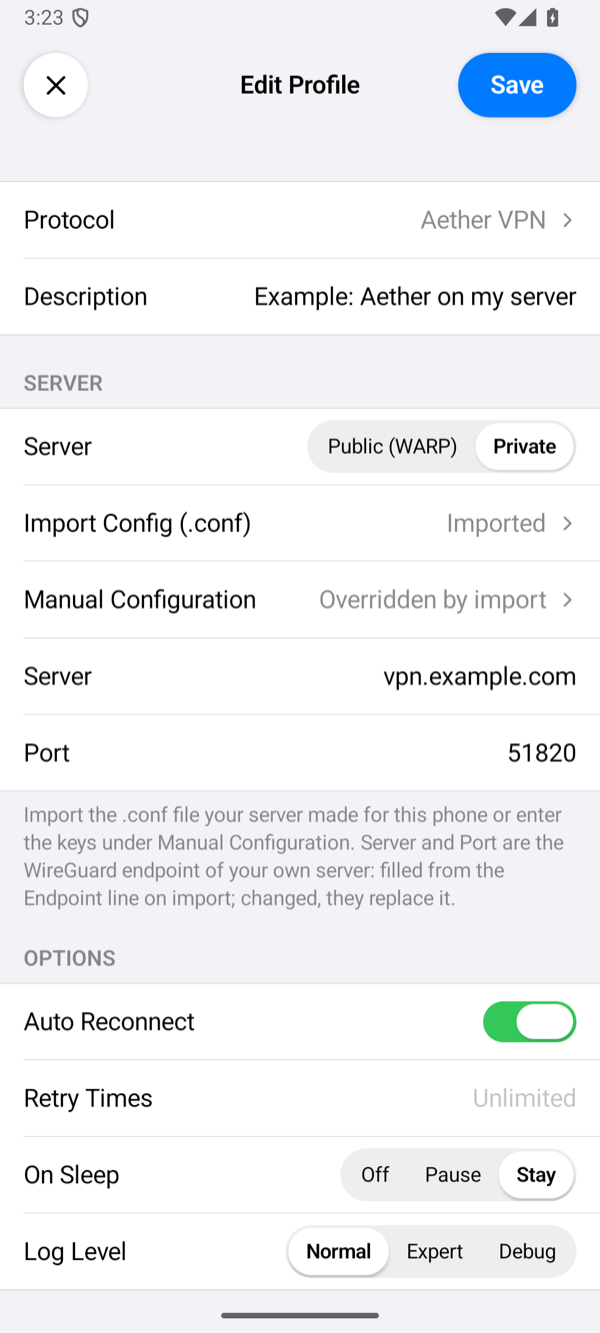
- Description: optional, the profile's name on the home screen. When it is empty, the home screen shows the server's name or address.
- Server: choose Private. The profile is then the phone's WireGuard connection to your server.
- Tap Import Config (.conf). It opens the phone's files: choose
phone1.conf. The row then says Imported, and Server and Port fill in from the file'sEndpointline: the name or address you put inendpoint=, and 51820. The file also brings the phone's keys, so leave Manual Configuration as it is: its row says Overridden by import. - Leave everything under Options as it is, and tap Save.
- Delete the copies of
phone1.confyou do not need, as part 6 says: the app keeps the file, on iPhone in the Keychain and on Android in its encrypted store.
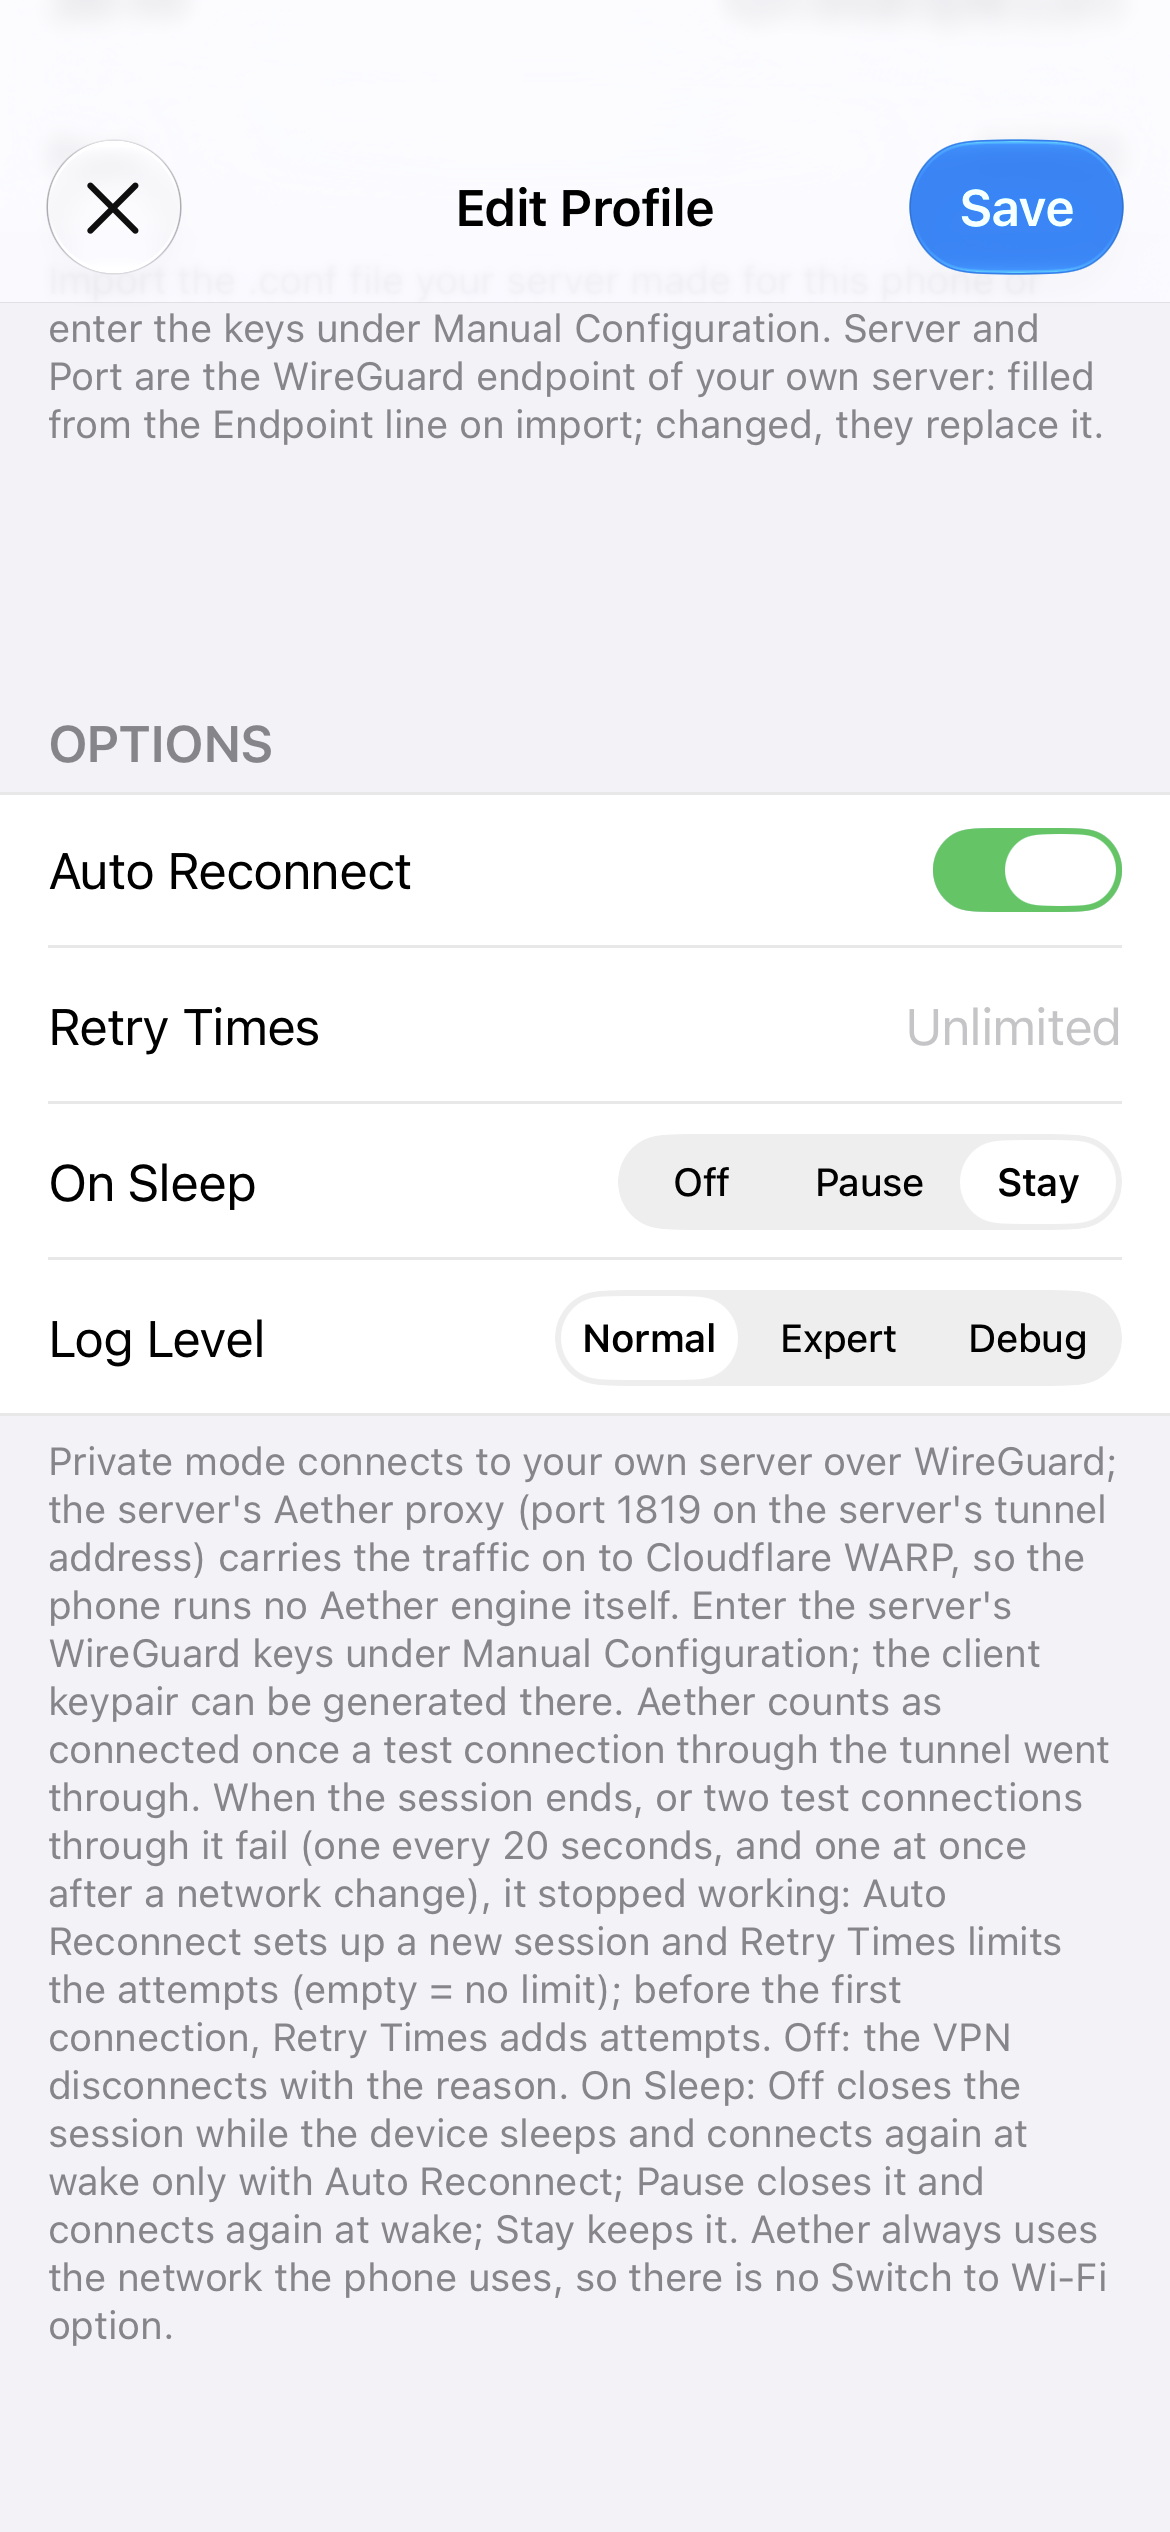
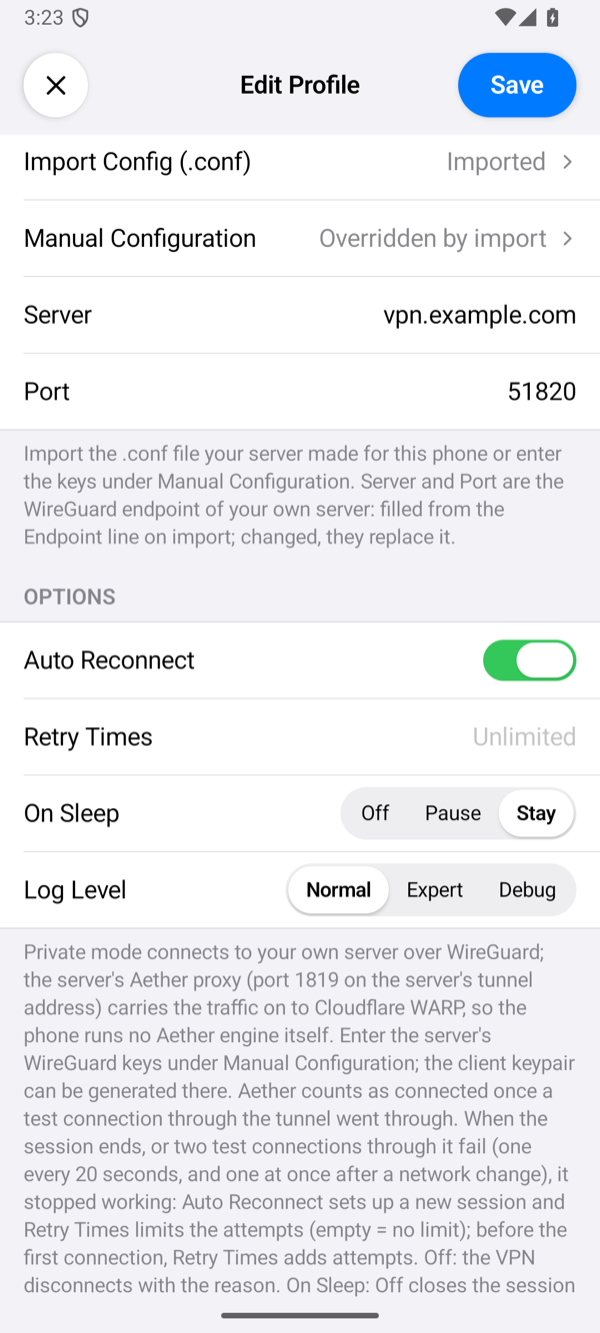
Connect
- On the home screen the profile shows your server and port. Select it and tap the power button.
- The first time, the system asks for permission: iOS asks whether the app may add a VPN configuration, and Android shows a Connection request. Allow it.
- The status changes to Connected once the first test connection through the tunnel has gone through, and the row of the profile then shows the time of one request through the tunnel.
wg show wg0, the peer whose allowed ips are 10.66.66.2/32, the address part 6 gave phone1, now has an endpoint, a latest handshake and its transfer; docker logs --tail 20 aether shows whether the engine has its tunnel to WARP; and the answer of the curl command has the line warp=on. If the app shows Connection Failed instead, tap the status under the power button to open the log, and see Troubleshooting, which explains each message of Private mode.
Setting up the app describes every field.