AmneziaWG server
This page sets up AmneziaWG on Ubuntu 24.04 for the app: our fork of amneziawg-go as the engine (the engine the app runs too) and the awg tools from the Amnezia packages, the server's keys and its own obfuscation values, its interface awg0, forwarding and NAT so the phones reach the internet through it, a configuration file for each phone that the app imports, and removing a phone again. Its last part sets up the profile in the app, on iPhone and on Android.
We ran these steps on our test server, Ubuntu 24.04 with Linux 6.8, 4 vCPUs and 4 GB of memory, on 9 November 2026, as the page shows them, with our server's name in place of vpn.example.com: the Amnezia packages gave us amneziawg-tools 3.1.20260812, Go fetched version 1.25.0 for the build, and the last line of part 1 printed amneziawg-go v3.1.20260828-srp.1. Then both phones connected with the page's phone1.conf, and phone2, removed as part 5 says, was refused (the awg-guide-… cases in Test results). Three things ran differently: our server had the kernel module before, and moved to our fork the same morning with the same commands, after apt purge amneziawg amneziawg-dkms and rmmod amneziawg instead of a restart, so part 1 found its packages already there; the ufw line of part 3 was not run, as ufw is not active on our server; and part 5 removed phone2, which we had added with part 4's script for that. After systemctl restart awg-quick@awg0 the server still had phone1 and its obfuscation values, as SaveConfig = true keeps them.
What you need
- An Ubuntu 24.04 server with a public IPv4 address, and root on it.
- A UDP port open to the phones; the page uses 51820, any free port works. A DNS name for the server is optional: the phones' files may name the server or its address.
1. Install
apt update
apt install -y software-properties-common
add-apt-repository -y ppa:amnezia/ppa
apt install -y amneziawg-tools golang-go git make
rm -rf /usr/local/src/amneziawg-go
git clone --branch v3.1.20260828-srp.1 --depth 1 https://github.com/bigmoveus/amneziawg-go /usr/local/src/amneziawg-go
cd /usr/local/src/amneziawg-go
GOTOOLCHAIN=auto make
make install
/usr/bin/amneziawg-go --version- The Amnezia packages bring
awgandawg-quick, the tools that configure AmneziaWG the waywgandwg-quickconfigure WireGuard;awg --versionprints their version. - The engine is amneziawg-go, AmneziaWG in userspace, built from our fork, github.com/bigmoveus/amneziawg-go: amneziawg-go's version of 28 August 2026 with a fix for data packets taken for handshake messages when
RandomTrailersis on and H1 to H3 are ranges (Configuration Reference). The app runs the same engine.make installputs it at/usr/bin/amneziawg-go, andawg-quickstarts it for each interface; the last line printsamneziawg-go v3.1.20260828-srp.1. - Ubuntu 24.04's Go is 1.22 and amneziawg-go asks for 1.25:
GOTOOLCHAIN=autolets Go fetch that version for the build. - The Amnezia packages also have a kernel module, in the
amneziawgpackage withamneziawg-dkms.awg-quicktakes the kernel module when it is there, and the module does not have the fix. If an earlier setup installed it, remove it withapt purge amneziawg amneziawg-dkmsand restart the server before part 2.
2. The server's keys and obfuscation values
cd /etc/amnezia/amneziawg
umask 077
awg genkey | tee server.key | awg pubkey > server.pub
awg genkey > header.key
S1=$(shuf -i 15-150 -n 1); S2=$(shuf -i 15-150 -n 1); S3=$(shuf -i 15-150 -n 1); S4=$(shuf -i 15-40 -n 1)
[ "$S2" -eq $((S1 + 56)) ] && S2=$((S2 + 1))
h() { start=$(( $1 * 1073741824 + $(shuf -i 5-1000000000 -n 1) )); echo "$start-$(( start + 50000000 ))"; }
cat > /etc/amnezia/amneziawg/awg0.conf <<EOF
[Interface]
Address = 10.67.67.1/24
ListenPort = 51820
PrivateKey = $(cat /etc/amnezia/amneziawg/server.key)
S1 = $S1
S2 = $S2
S3 = $S3
S4 = $S4
H1 = $(h 0)
H2 = $(h 1)
H3 = $(h 2)
H4 = $(h 3)
HeaderProtectionKey = $(cat /etc/amnezia/amneziawg/header.key)
MTU = $((1420 - S4))
SaveConfig = true
PostUp = iptables -I FORWARD 1 -i %i -j ACCEPT; iptables -I FORWARD 2 -o %i -m conntrack --ctstate RELATED,ESTABLISHED -j ACCEPT; iptables -t nat -A POSTROUTING -s 10.67.67.0/24 -o ens160 -j MASQUERADE
PostDown = iptables -D FORWARD -i %i -j ACCEPT; iptables -D FORWARD -o %i -m conntrack --ctstate RELATED,ESTABLISHED -j ACCEPT; iptables -t nat -D POSTROUTING -s 10.67.67.0/24 -o ens160 -j MASQUERADE
EOFserver.keyis the server's private key andserver.pubits public key, which every phone's file names;header.keyis the key of header protection.umask 077keeps them readable by root only.- S1 to S4 are the random bytes put in front of the handshake's first message, its answer, a cookie message and every data packet; H1 to H4 are the ranges the four message types draw their first four bytes from, instead of WireGuard's fixed 1 to 4. Together they take away WireGuard's fixed sizes and headers. The commands pick values of this server's own: random paddings (S2 never 56 more than S1, which would give the first two messages the same size) and four ranges of 50,000,001 values, one in each quarter of the 32-bit numbers, so they never overlap. The phones must have the same values: part 4 copies them into each phone's file.
- HeaderProtectionKey (AmneziaWG 3) encrypts the parts of each packet's header that WireGuard sends in the clear; the phones need the same key.
MTUis 1420 less S4: S4 makes every data packet longer, and with this MTU a full packet still fits a 1500-byte path, as WireGuard's own does with 1420.Address = 10.67.67.1/24is the server's address inside the tunnel; the phones get the other addresses of 10.67.67.0/24.SaveConfig = trueletsawg-quick savewrite the phones that part 4 adds back into this file, so they come back after a restart.- The
PostUplines let the phones' traffic through the server and replace their addresses with the server's on the way out;PostDowntakes the rules away.ens160is the name of our server's network interface;ip route show defaultprints yours afterdev.
echo 'net.ipv4.ip_forward = 1' > /etc/sysctl.d/60-amneziawg.conf
sysctl -p /etc/sysctl.d/60-amneziawg.conf
systemctl enable --now awg-quick@awg0
awg show awg0
awg show prints the interface with its public key, listening port: 51820 and its obfuscation values.
3. Firewall
Open UDP port 51820 to the phones. If ufw is active: ufw allow 51820/udp. The PostUp rules of part 2 already let the phones' traffic through.
4. A file for each phone
Each phone gets its own key pair and its own preshared key, which adds a second secret to the handshake. This script makes them, adds the phone to awg0 and writes the file the app imports, with the server's obfuscation values and three of the phone's own: Jc junk packets of Jmin to Jmax random bytes that the phone sends before every handshake. Save it as /etc/amnezia/amneziawg/add-phone.sh and put your server's name or address in endpoint=:
#!/bin/bash
# add-phone.sh NAME NUMBER: a key pair and a preshared key for the phone NAME, its peer on awg0 with the address
# 10.67.67.NUMBER, and /etc/amnezia/amneziawg/clients/NAME.conf, the file the app imports.
set -euo pipefail
name=$1; number=$2; endpoint=vpn.example.com:51820
cd /etc/amnezia/amneziawg
umask 077
mkdir -p clients
private=$(awg genkey); public=$(echo "$private" | awg pubkey); psk=$(awg genpsk)
echo "$public" > "clients/$name.pub"
awg set awg0 peer "$public" preshared-key <(echo "$psk") allowed-ips "10.67.67.$number/32"
awg-quick save awg0
cat > "clients/$name.conf" <<EOF
[Interface]
PrivateKey = $private
Address = 10.67.67.$number/32
DNS = 1.1.1.1, 8.8.8.8
Jc = 4
Jmin = 40
Jmax = 70
$(grep -E '^(S[1-4]|H[1-4]|HeaderProtectionKey|MTU) = ' awg0.conf)

[Peer]
PublicKey = $(cat server.pub)
PresharedKey = $psk
Endpoint = $endpoint
AllowedIPs = 0.0.0.0/0
PersistentKeepalive = 25
EOF
echo "/etc/amnezia/amneziawg/clients/$name.conf"
chmod 700 /etc/amnezia/amneziawg/add-phone.sh
/etc/amnezia/amneziawg/add-phone.sh phone1 2- It prints the file's name, here
/etc/amnezia/amneziawg/clients/phone1.conf. The file holds the phone's private key: whoever has it can connect as that phone. Copy it to the phone and import it in the app (Import Config), then delete the copies you do not need. AllowedIPs = 0.0.0.0/0sends all of the phone's IPv4 traffic through the VPN, andDNSnames the name servers it uses meanwhile.PersistentKeepalive = 25makes the phone send a keepalive every 25 seconds when nothing else goes, so routers between the phone and the server keep its path open. Configuration Reference explains these and the other settings AmneziaWG has.- Give each phone its own number, and its own file: one key on two phones does not work, as with WireGuard.
5. Removing a phone
This script takes a phone off awg0 at once and out of the saved configuration; save it as /etc/amnezia/amneziawg/remove-phone.sh:
#!/bin/bash
# remove-phone.sh NAME: the phone NAME off awg0 and out of awg0.conf, and its files deleted.
set -euo pipefail
name=$1
cd /etc/amnezia/amneziawg
awg set awg0 peer "$(cat "clients/$name.pub")" remove
awg-quick save awg0
rm -f "clients/$name.pub" "clients/$name.conf"
chmod 700 /etc/amnezia/amneziawg/remove-phone.sh
/etc/amnezia/amneziawg/remove-phone.sh phone2The server answers nothing to a key it does not know, so a removed phone cannot connect: the app waits for the handshake and then reports that the server did not answer it.
6. Check
awg show awg0Each phone is a peer with its allowed ips. A phone that connected has an endpoint (the address it came from), a latest handshake (renewed every 2 minutes while traffic flows) and its transfer.
7. Set up the app on the phone
An AmneziaWG profile has the same fields on iPhone and Android; where the two phones differ, the steps say so. Install the app first: on iPhone from TestFlight (Installation), on Android by building it from the source (Installation). Where to start says which build to use.
Create the profile
- Copy
/etc/amnezia/amneziawg/clients/phone1.conf, the file part 4 made, to the phone. - On the home screen, tap +.
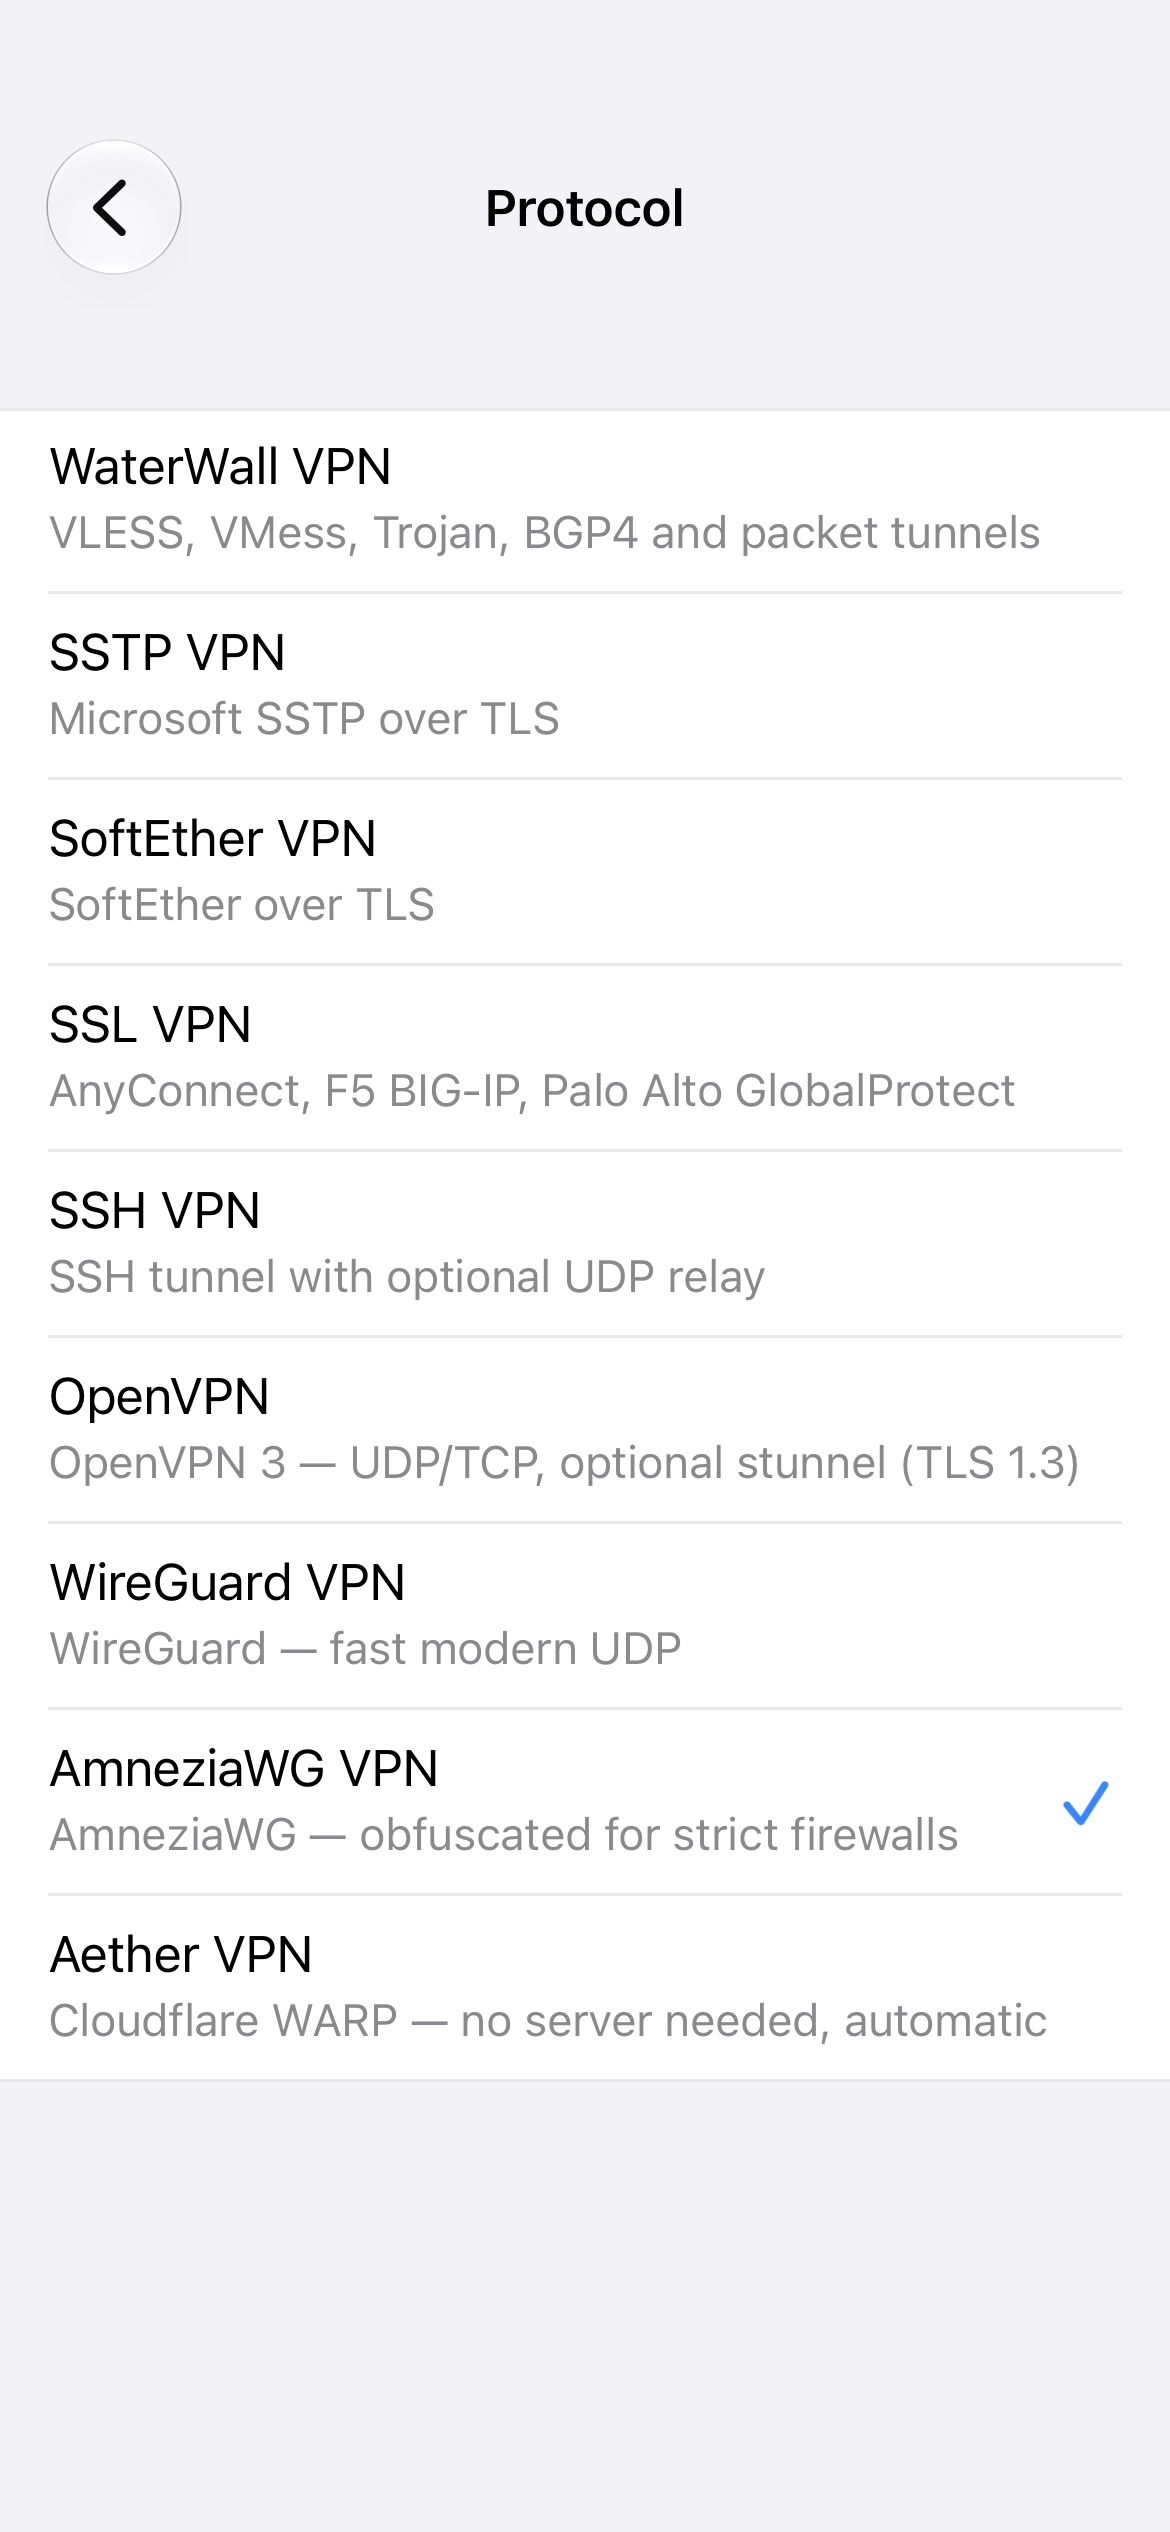
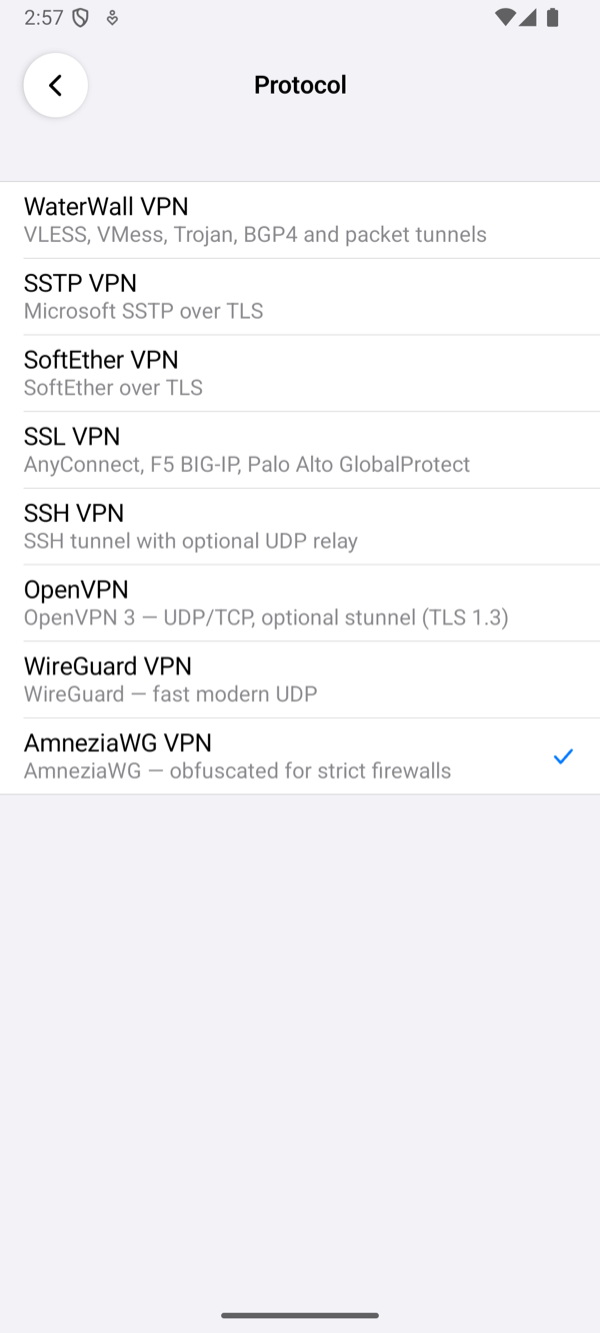
- Tap Protocol and choose AmneziaWG VPN.
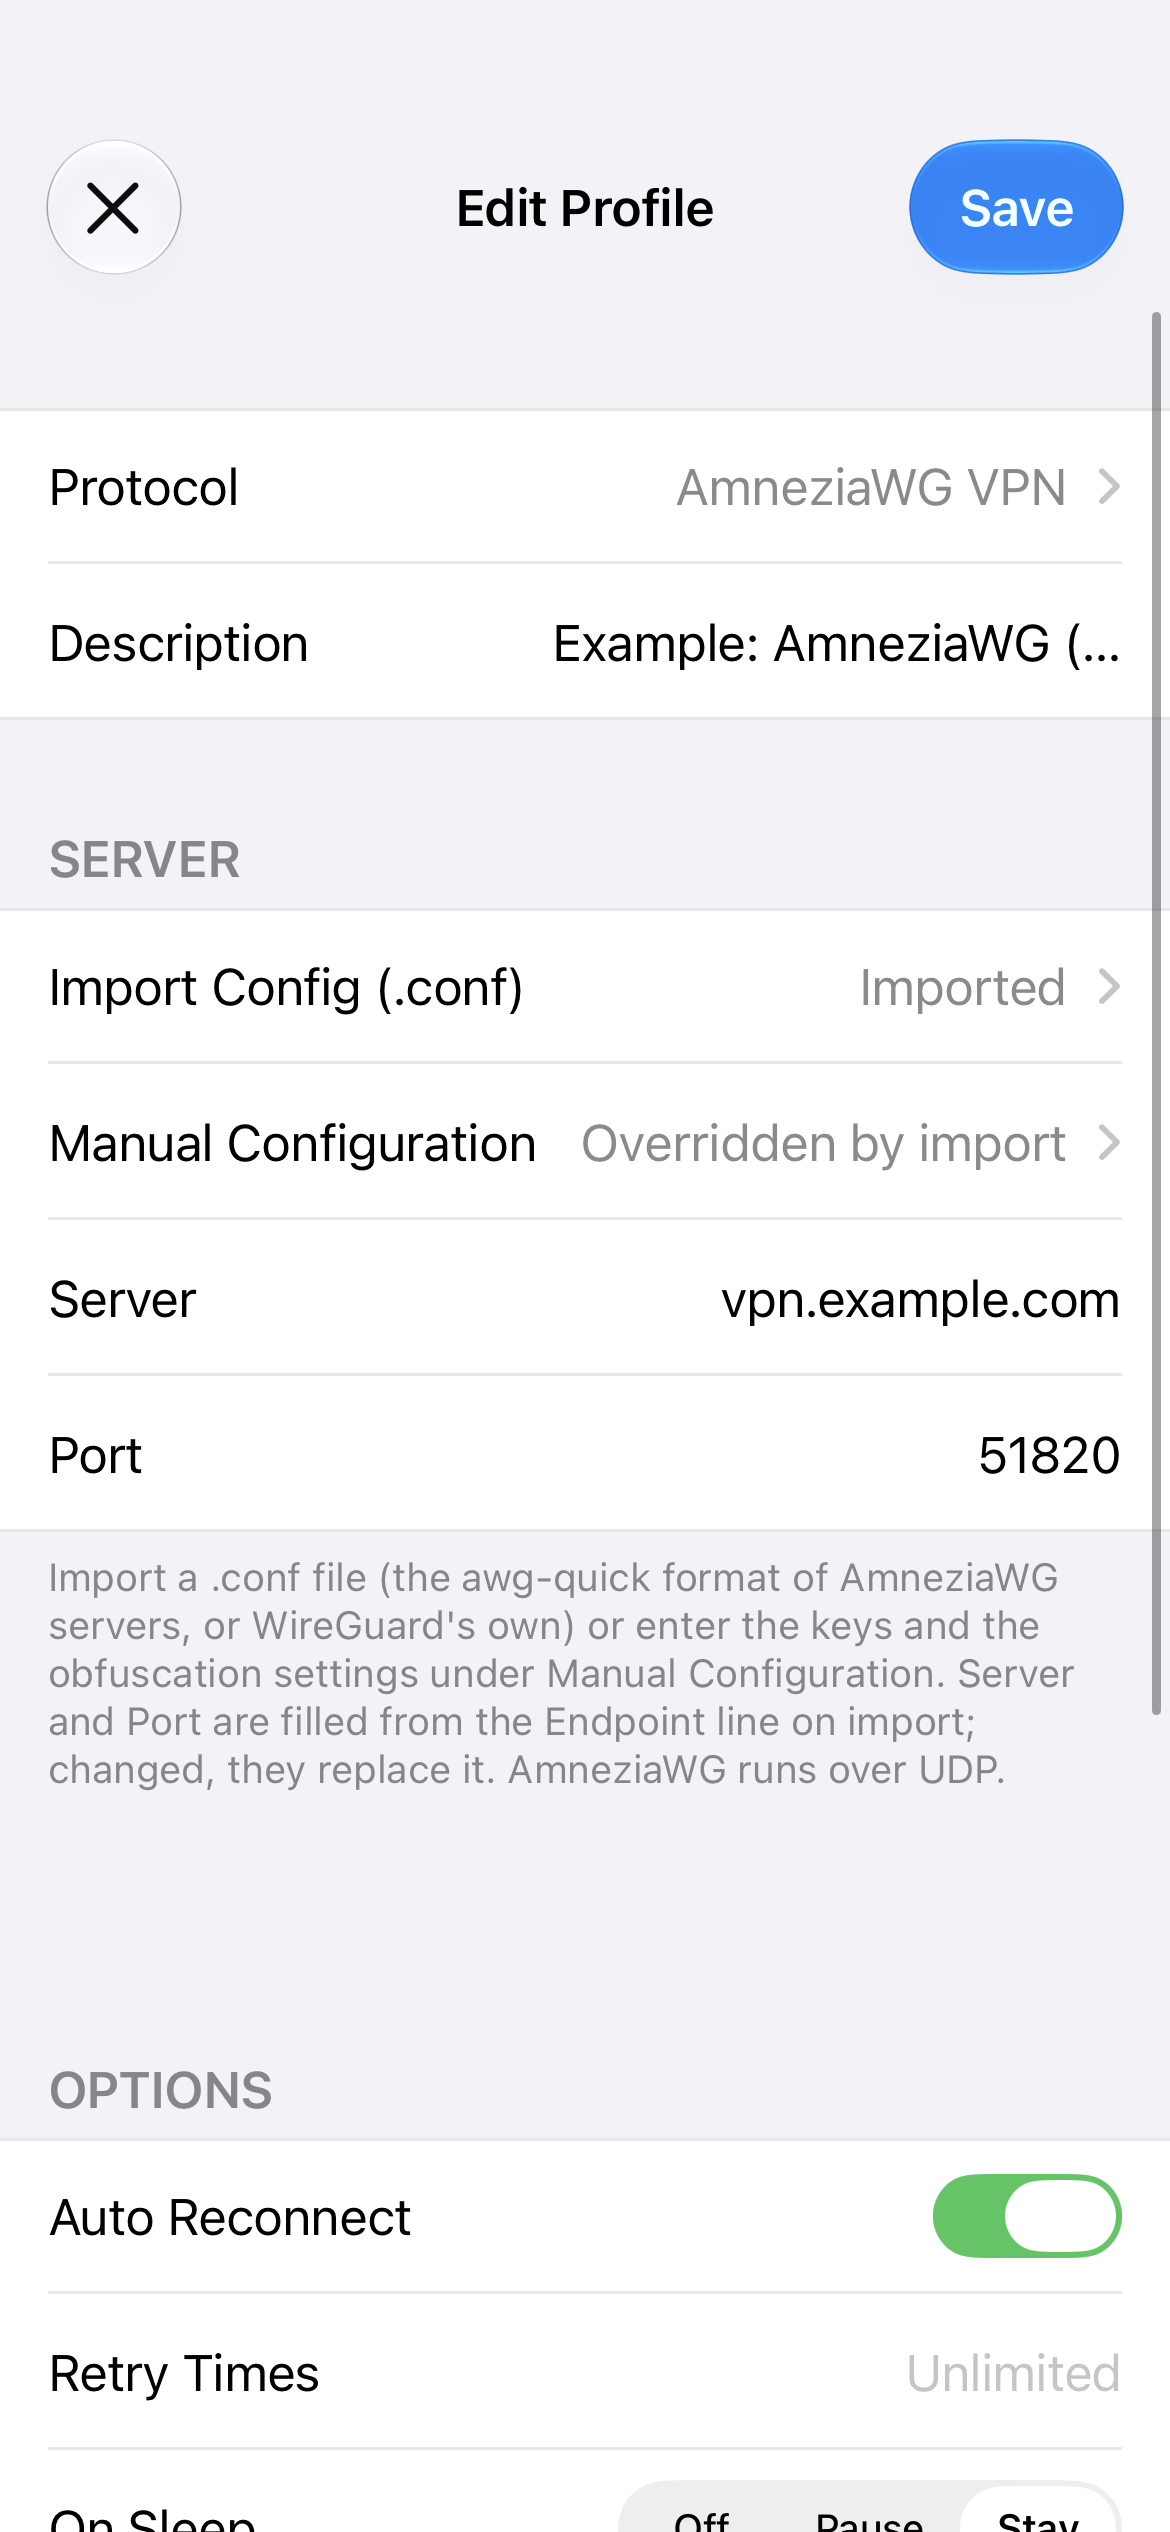
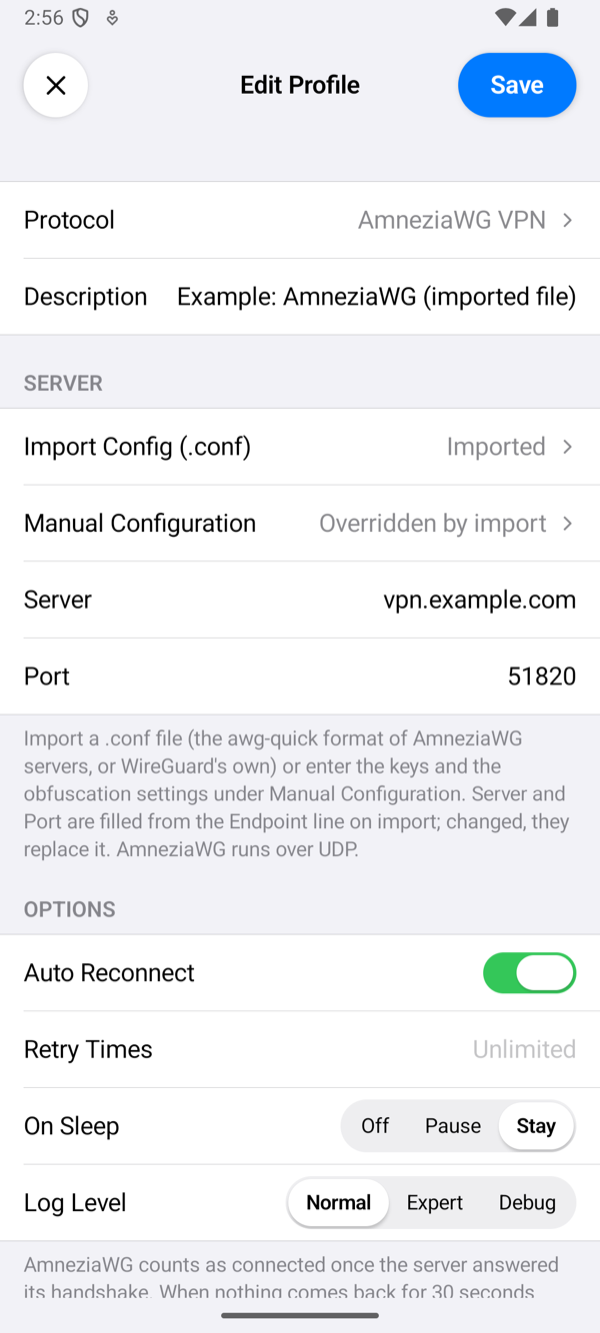
- Description: optional, the profile's name on the home screen. When it is empty, the home screen shows the server's name or address.
- Tap Import Config (.conf). It opens the phone's files: choose
phone1.conf. The row then says Imported, and Server and Port fill themselves in from the file'sEndpointline: the name or address you put inendpoint=, and 51820. The file also brings the phone's keys, the server's obfuscation values of part 2 and the phone's Jc, Jmin and Jmax, so leave Manual Configuration as it is: its row says Overridden by import. - Leave everything under Options as it is, and tap Save.
- Delete the copies of
phone1.confyou do not need, as part 4 says: the app keeps the file, on iPhone in the Keychain and on Android in its encrypted store.
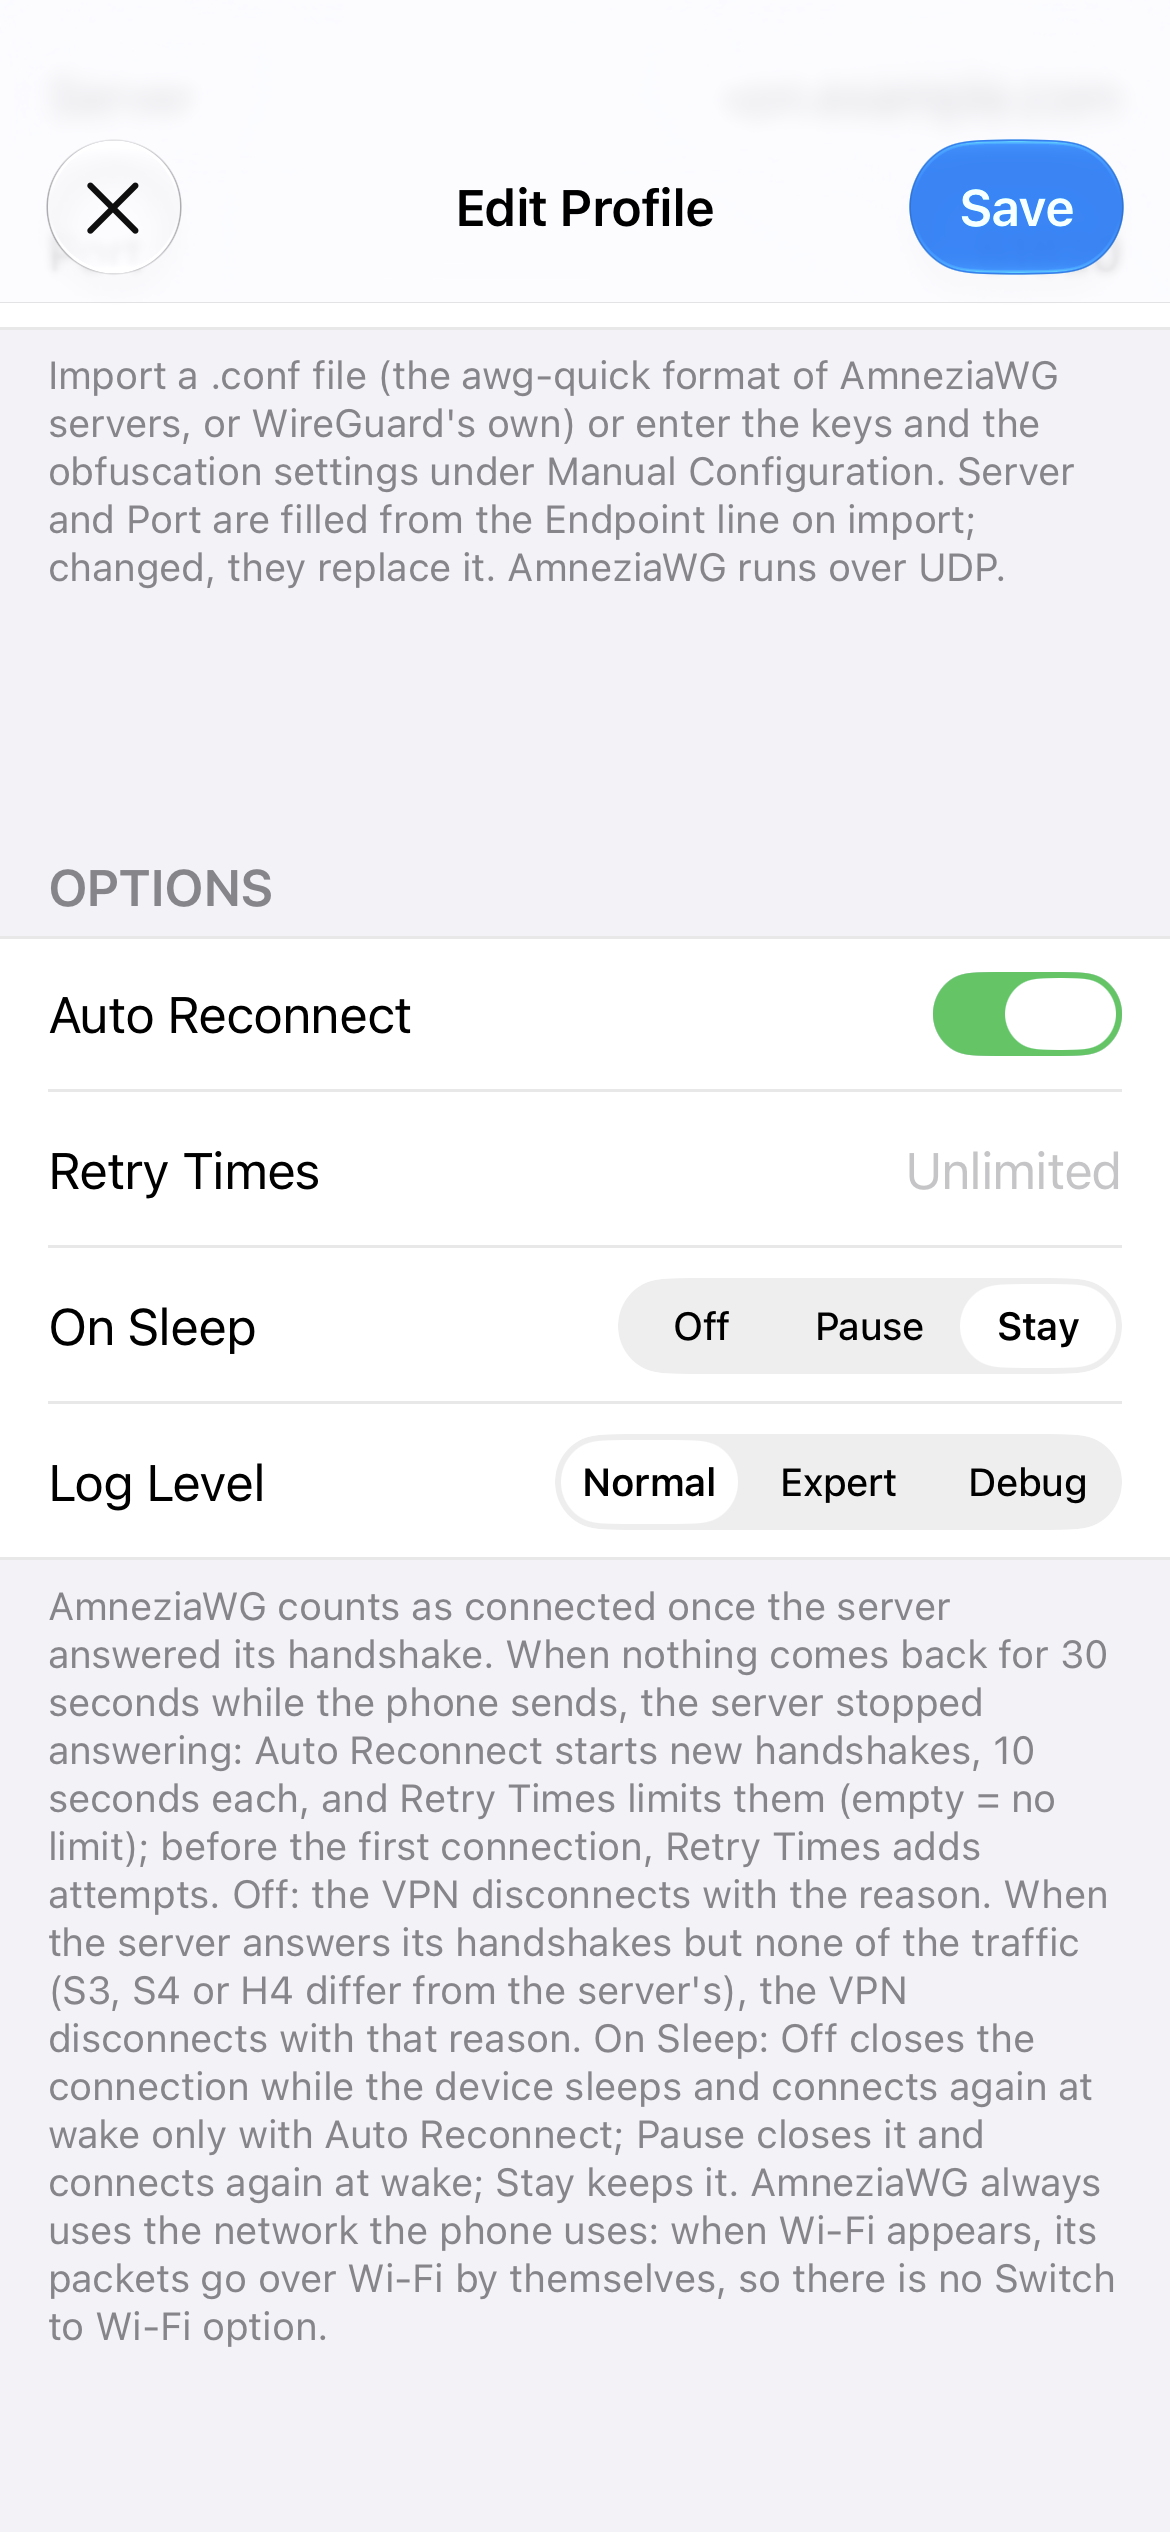
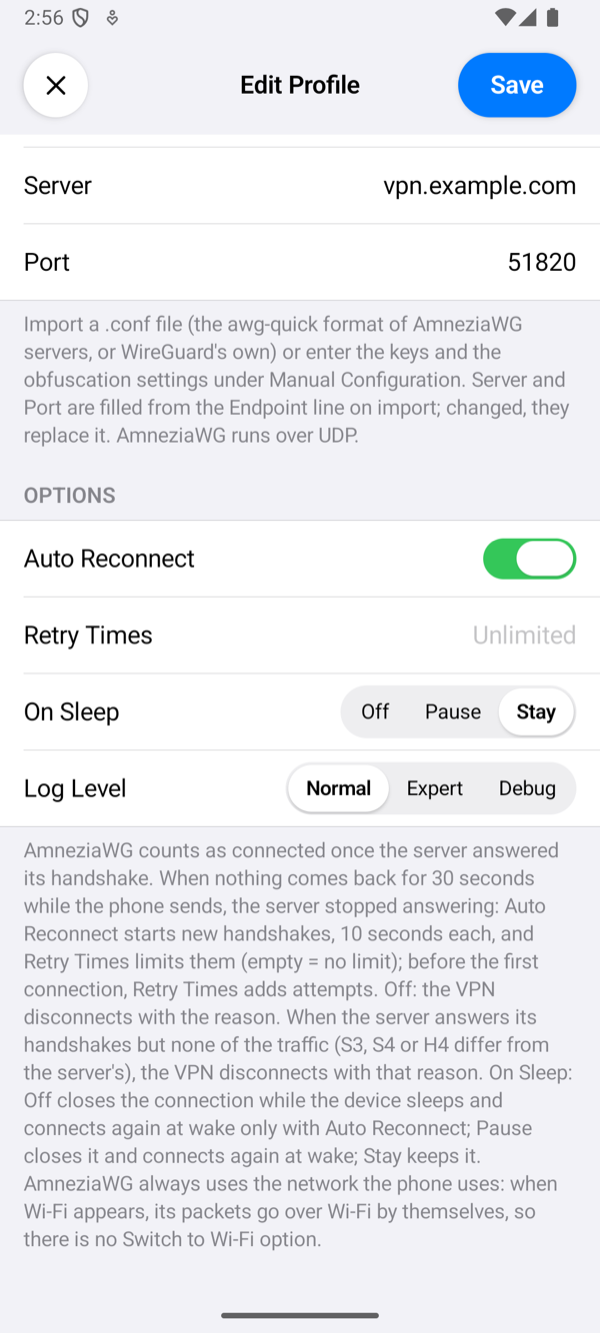
Connect
- Select the profile on the home screen and tap the power button.
- The first time, the system asks for permission: iOS asks whether the app may add a VPN configuration, and Android shows a Connection request. Allow it.
- The status changes to Connected once the server has answered the handshake, and the row of the profile then shows the time of one request through the tunnel.
awg show awg0 as in part 6: the peer whose allowed ips are 10.67.67.2/32, the address part 4 gave phone1, now has an endpoint, a latest handshake and its transfer. If the app shows Connection Failed instead, tap the status under the power button to open the log, and see Troubleshooting, which explains each message.
Setting up the app describes every field.